You can invite users in your organization tenant to help manage the portal, and choose exactly what each user is allowed to do. This guide walks you through management of managing that access.
About 3 minutes | Administrator access needed | User Access
Before you start
- You're signed in to the admin management portal.
- You know who you want to give access to, and what they'll need to do.
- That person already has an account in your organizationEntra tenant.
...
Assign Role
From the Dashboard, click User Access. This page lists everyone who currently has access, split into Groups and Users.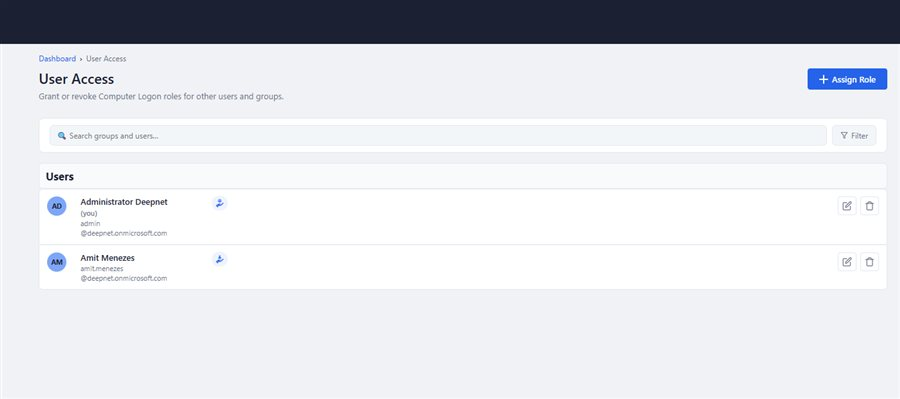
The User Access page
Step 2: Click "Assign Role" and find them
To assign a role to a user or user group, click the Assign Role button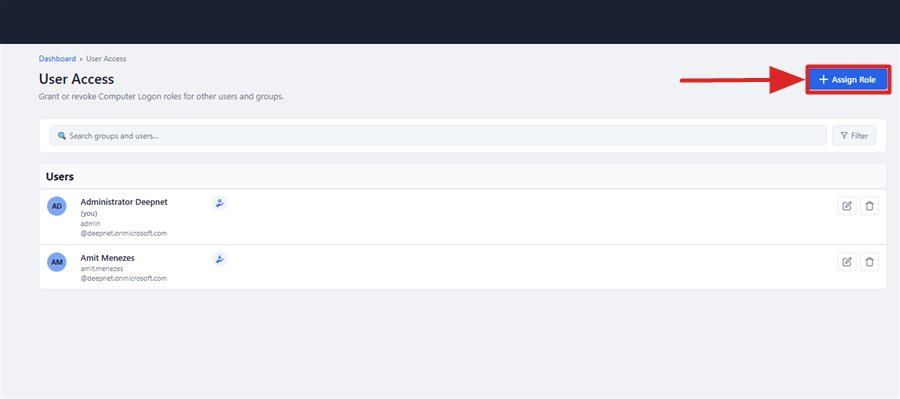
The Assign a role window will pop up
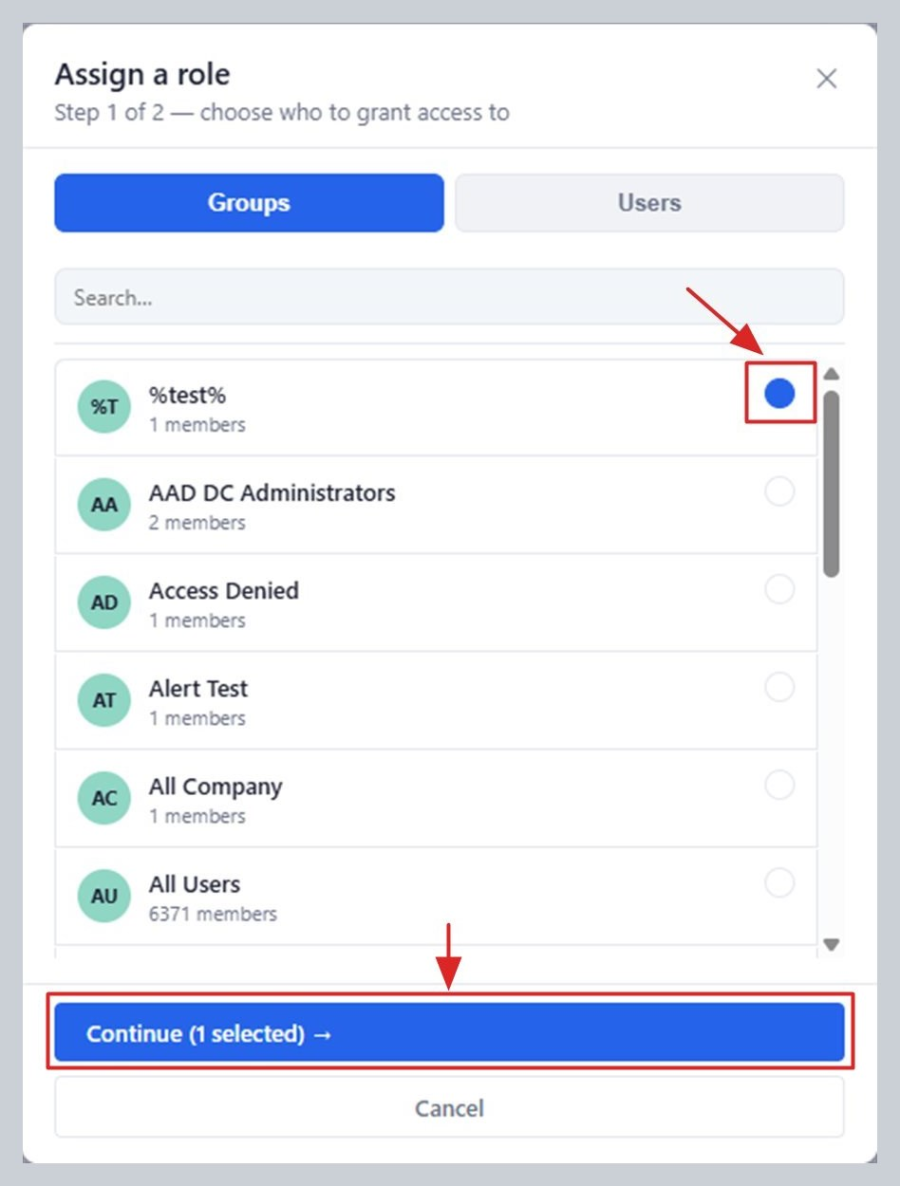
Select the user(s) or user group(s) you want A window opens — step 1 of 2. Switch between the Groups and Users tabs, type a name into the search box, and click a result to select it. You can select more than one person or group at once. Click Continue →.
Click the highlighted "Assign Role" button
Select who to grant access to, then click "Continue →"
...
Now, you need to choose the level of access
...
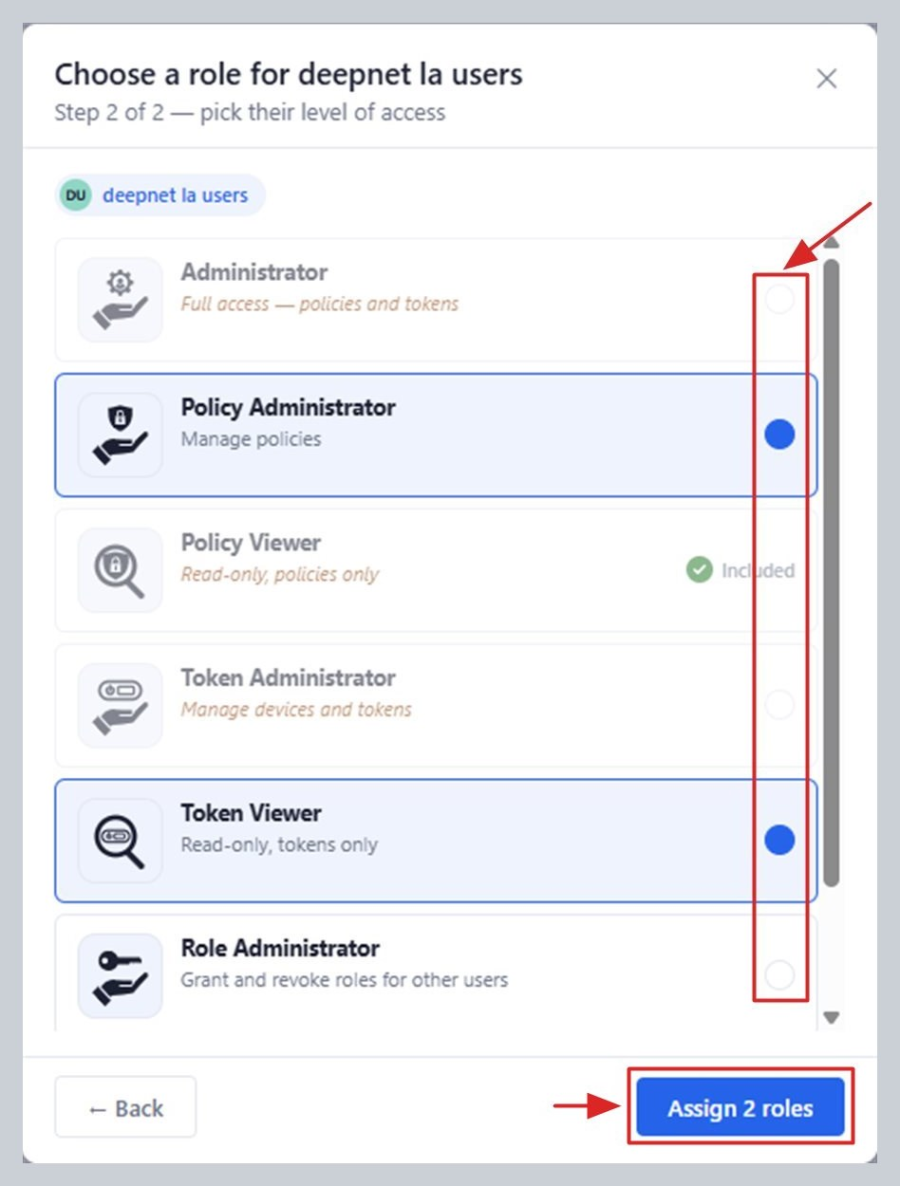
Select Step 2 of 2 — tick one or more roles. Only give someone as much access as they actually need.
Click Assign. That person (or everyone in the group) can now sign in to the portal themselves and use whatever you gave them access to — there's nothing else for them to set up.
| Expand | ||
|---|---|---|
| ||
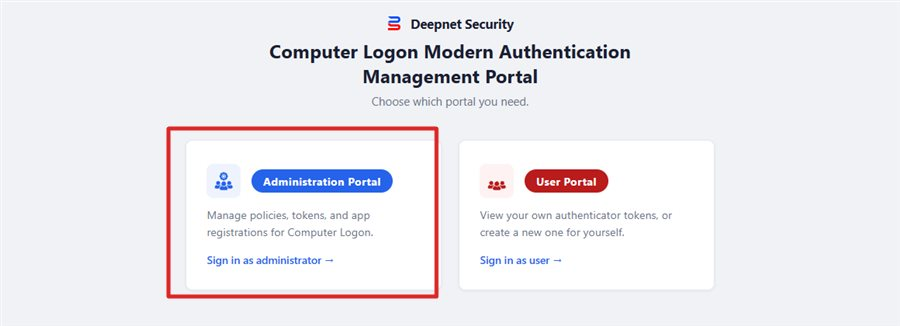
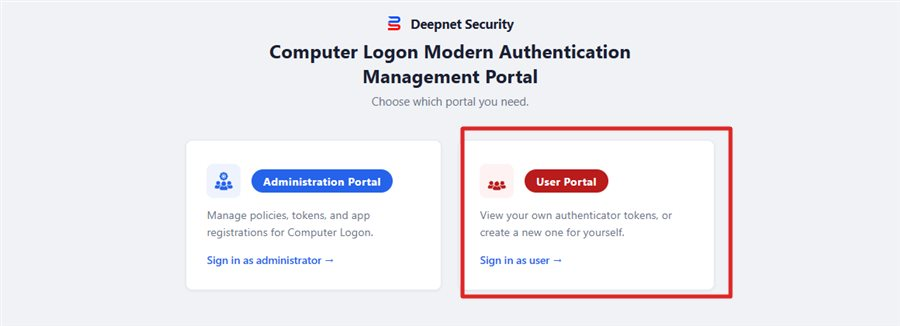
There are two access portals provided by the management portal — |
...
the Administration Portal and the self-service User Portal. |
...
...
Administration Portal |
...
Portal has the following access roles:
|

...
...
User Portal |
...
|
...
The portal has the following access roles:
|

...
. |
...
...
Change or remove access
...
roles
Back on the User Access page, each row has:
...
ℹ️ Can only grant or remove a role with Role Administrator. Can only be done to a user with matching Policy and Token management roles already held by the access granting/removing user.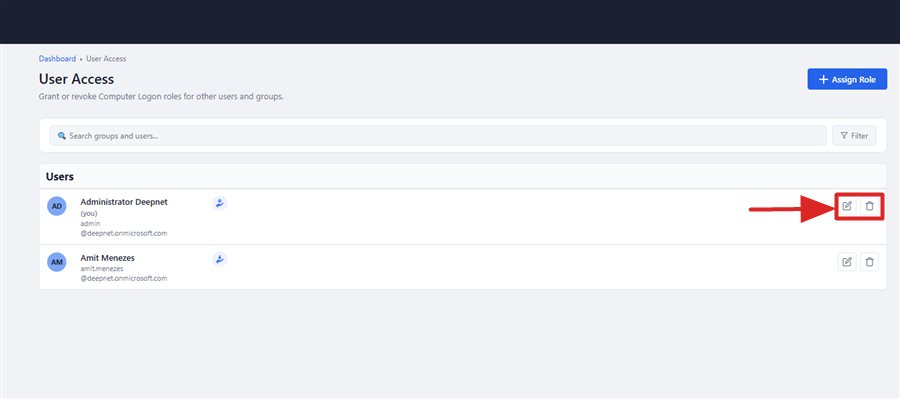
The Edit access and Delete icons on each row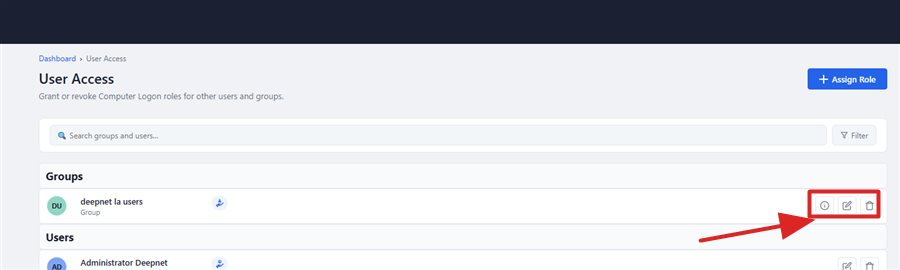
Groups and users are listed in their own sections, each with matching row actions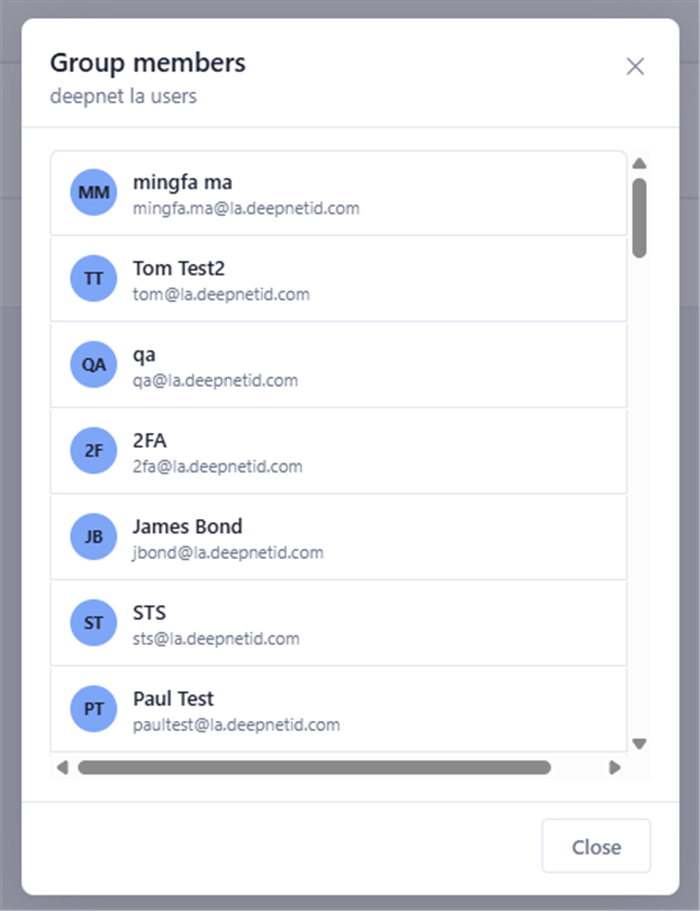
Clicking Info shows the group's real members
That's it
You've given someone access to the portal, with exactly the level of control you chose for them. Check back on the User Access page from time to time to make sure only the right people still have access.